
Phishing-resistant MFA for hospitals
Phishing-resistant MFA for hospitals is sign-in that a fake login page cannot steal: FIDO2 passkeys or certificates held in hardware and unlocked with a PIN or fingerprint. The Crayonic Badge delivers it as a security-first wearable clinicians wear all shift. It signs them in to shared workstations by presence and locks the session when they walk away.
Book a Demo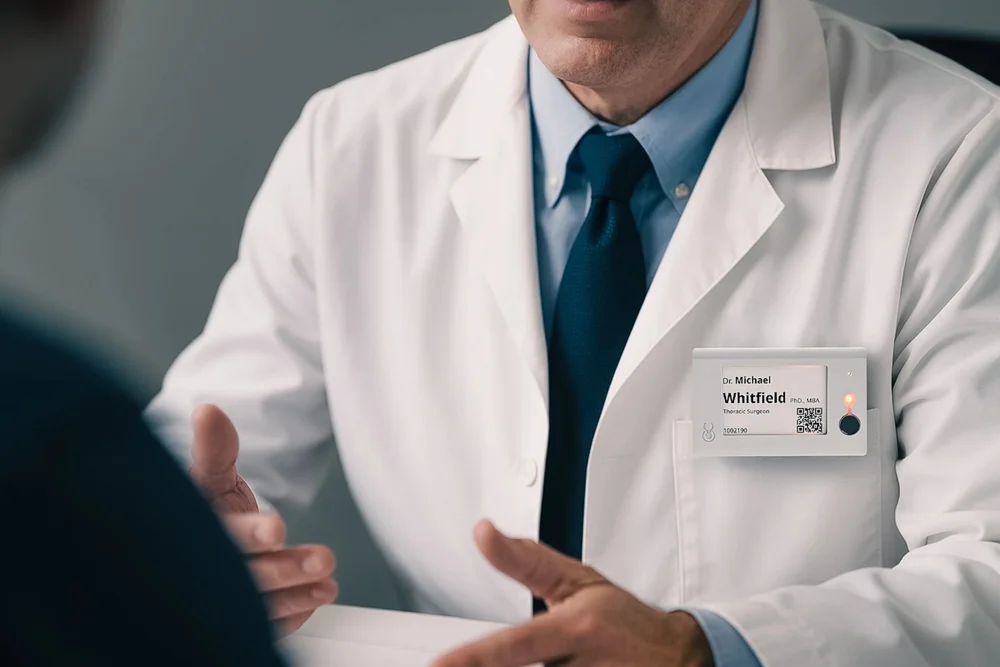
Why codes and push prompts are not enough
CISA calls phishing-resistant MFA “the gold standard for MFA” and names FIDO/WebAuthn as its most widely available form. One-time codes and push approvals can be relayed by reverse-proxy phishing kits together with the password and session cookie, and push prompts can be spammed until a tired user approves one. A FIDO2 credential is bound to the real website’s domain, so a look-alike page gets nothing it can reuse.
What regulators now expect
EU: NIS2 Article 21
Health is a sector of high criticality. Required measures include “the use of multi-factor authentication or continuous authentication solutions”.
England: NHS MFA policy
Strong MFA on all remote access. Exceptions on clinical grounds must be documented, risk-assessed and approved at board level.
England: NHS CIS2
“Staff on shared devices, desktops or kiosks can use smartcards or security keys”, each registered to the individual.
Why most phishing-resistant MFA breaks on a ward
Shared PCs
Windows Hello for Business supports at most 10 enrollments per device, and Shared PC mode turns it off. A ward PC with two shifts, locums and students is over the limit by design.
Synced passkeys
They follow a personal or shared cloud account, not the clinician standing at the PC.
USB keys
Keys stay in the port, and the session stays open when the clinician walks off.
Speed
A 105-second login gets bypassed. Alder Hey cut it to 10 seconds and saved over 130 staff hours a day. Read the analysis.
How the Crayonic Badge does it
- Strong once per shift. The clinician unlocks the Badge with a PIN on its own screen or a fingerprint, so no keylogger or fake page ever sees either.
- Touchless after that. A Crayonic Bridge at each workstation signs them in as they approach and out as they leave. Where only an NFC reader exists, they tap the Badge like a smart card.
- One identity per person. FIDO2 passkeys and X.509 certificates sit in a Common Criteria EAL5+ secure element, registered in Microsoft Entra ID or Active Directory.
- Works offline. Login keeps working during internet or cloud outages, and device and credential management can run fully on-premises.
Checklist for choosing hospital MFA
| Requirement | Why it matters on a ward |
|---|---|
| One identity per person | Every action in the record has a name; no shared ward accounts. |
| Seconds per login, measured | Slow logins get bypassed. Count logins per shift and seconds per login before and after. |
| Lock on walk-away | No long timeouts to defeat with workarounds. |
| No personal phone needed | Works with gloves and masks, and for staff without a work phone. |
| Logged break-glass access | Emergency access exists and is reviewed afterwards. |
| FIDO2-certified hardware | The credential is phishing-resistant and cannot be copied off the device. |
Comparing options? See Crayonic Badge vs YubiKey and Crayonic vs Imprivata.
Frequently asked questions
What counts as phishing-resistant MFA?
FIDO2/WebAuthn passkeys and PKI certificates held in hardware. SMS codes, authenticator-app codes and push approvals do not count.
Can phishing-resistant MFA be fast enough for clinicians?
Yes, if the strong step happens once per shift and later logins are touchless. With the Crayonic Badge, the clinician walks up to the workstation and is signed in.
Does it work on shared workstations?
Yes. Each clinician carries their own credentials on the Badge, so any number of staff can use the same PC.
Is the Crayonic Badge certified?
The Badge is FIDO2 Level 1 certified, and FIDO2 Level 2 certification is expected in H1 2027. Keys and fingerprint templates stay in a Common Criteria EAL5+ secure element.
Does it help with NIS2?
It provides the phishing-resistant multi-factor authentication and the audit trail that NIS2 Article 21 asks for. Full compliance also depends on your wider policies and systems.
See it on your ward
Book a 30-minute demo, or ask for a pilot kit with Badges and Bridges for one unit.
Book a DemoExplore the Badge